Skip to content

Serving all of Qatar

Continuity & Resilience · Disaster Recovery

Disaster recovery & operational resilience

If a major incident affects your main site, critical security operations and evidence should survive. FISSS designs replication, standby operation and tested recovery procedures.
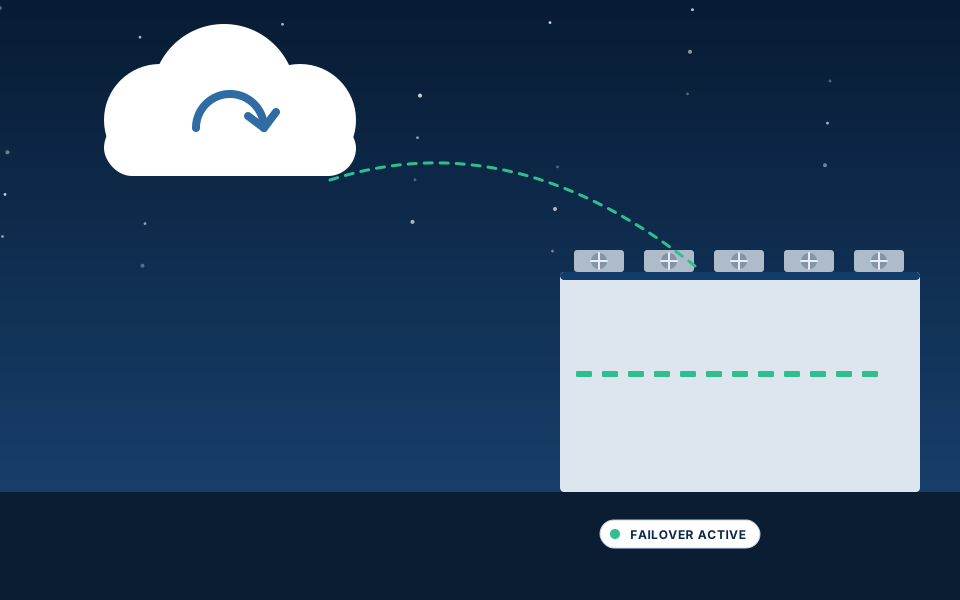
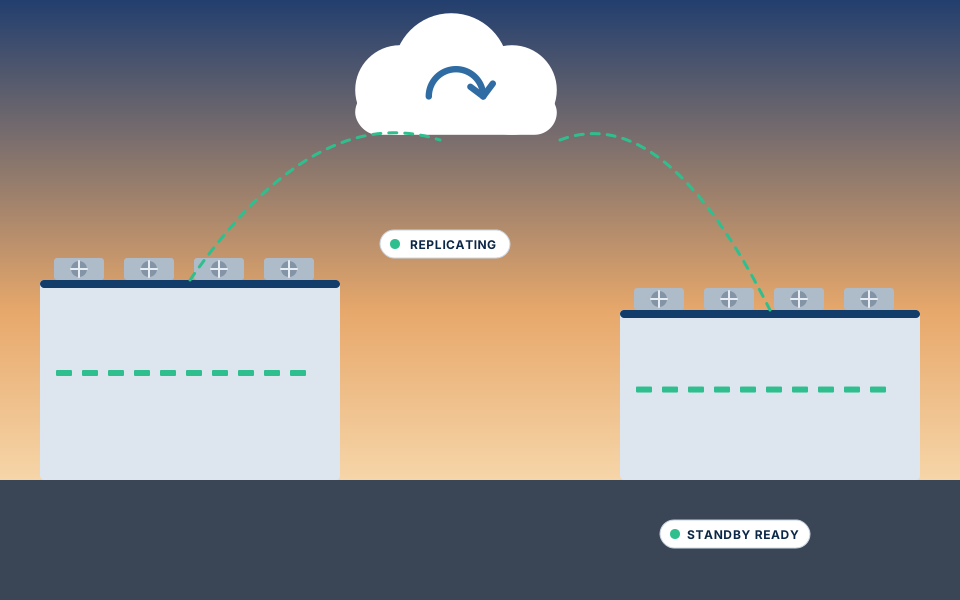
Secondary site taking over monitoring after an incident

Why Disaster Recovery matters for your facility

We agree recovery objectives with you — how much data can be lost and how quickly operations must resume — then design replication of databases, configurations and critical video to a secondary location. Standby consoles and documented procedures let operators resume monitoring, and regular drills confirm that recovery works.

Disaster Recovery key specifications

ReplicationEncrypted replication to a secondary site
EncryptionAES-256 for data in transit and at rest
StandbySecondary operator consoles and recovery procedures
ArchivesTamper-resistant evidence archives where required

Aligned with ISO 22301 and ISO/IEC 27001 principles and National Cyber Security Agency guidance.

Replication from the main control room to a standby site

What our Disaster Recovery scope includes

Where we install Disaster Recovery

Disaster Recovery engineering considerations

Agree the objectives

Recovery point and recovery time objectives drive the design and cost.

Protect the evidence

Encrypted, access-controlled archives preserve the integrity of recordings.

Practise the plan

A recovery plan that has never been exercised rarely works under pressure.

Disaster Recovery questions answered

Not always. Many sites replicate system databases, configurations and selected critical cameras, balancing protection with bandwidth.

At least annually, and after major system changes.

Ready to scope your Disaster Recovery project?

Share floor plans, a BOQ or a short brief. Our engineers will size the Disaster Recovery design, recommend suitable equipment and confirm the next step for your site.